Official Netflix Qr Code vs Phishing Fake: Visual Clues to Protect Your Credentials
 By Sophia Al-Mansoor
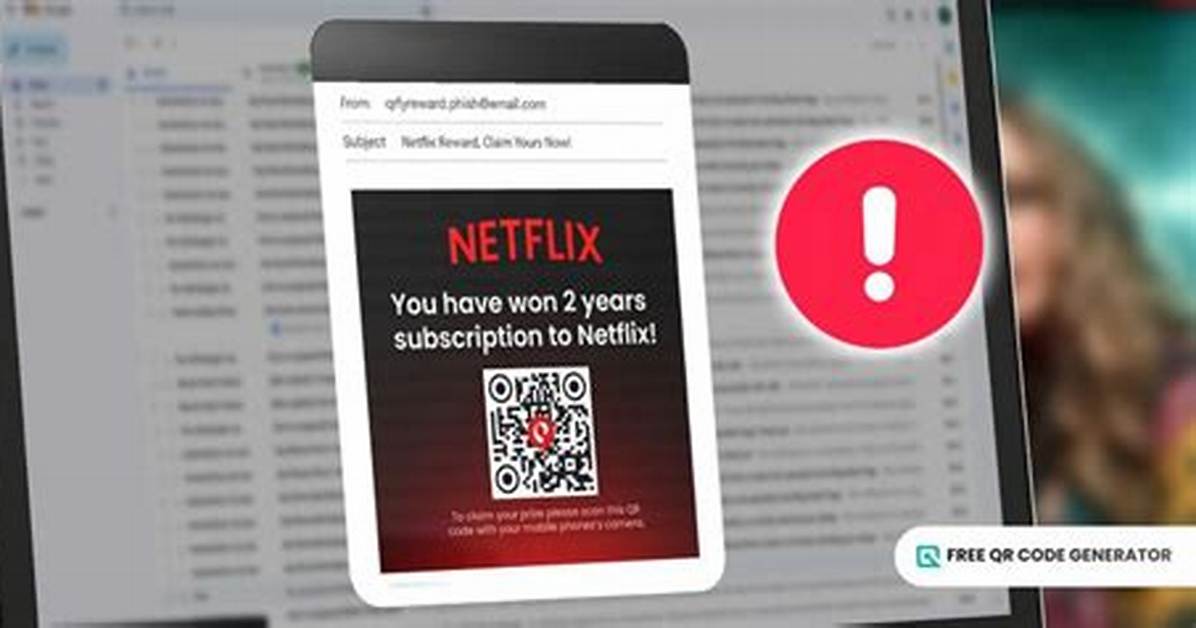
The rise of QR-based authentication was supposed to eliminate the headache of pecking out 16-character alphanumeric passwords with a clunky television remote. When Netflix deployed its automated pairing architecture, it let subscribers scan an on-screen matrix barcode with a smartphone camera, instantly linking the television to an active mobile session. But usability often creates blind spots.
Following the global rollout of the Netflix Household update, millions of viewers faced unexpected logouts across secondary sets, hotel devices, and mobile hardware. Security research published by McAfee in early 2026 underscored how threat actors seized upon this operational confusion. Instead of targeting network routers directly, scammers targeted subscriber impatience.
Because QR codes obscure URLs from human eyes until decoded, victims scan without scrutinizing the underlying payload. Fraud rings deploy these barcodes through targeted phishing emails, rogue pop-ups on third-party smart TV operating systems, and even physical stickers placed on rental property entertainment systems. The objective remains singular: steer the user away from the secure ecosystem and into a hostile credential harvesting pipeline.
Sophia analyzes international trade, startup ecosystems, retail transformation, and supply chain logistics for modern digital publications.
