Discord Gg Inpvp Legitimacy Check: Screenshots, Link Audit, and Safety Proof
 By Marcus Vance
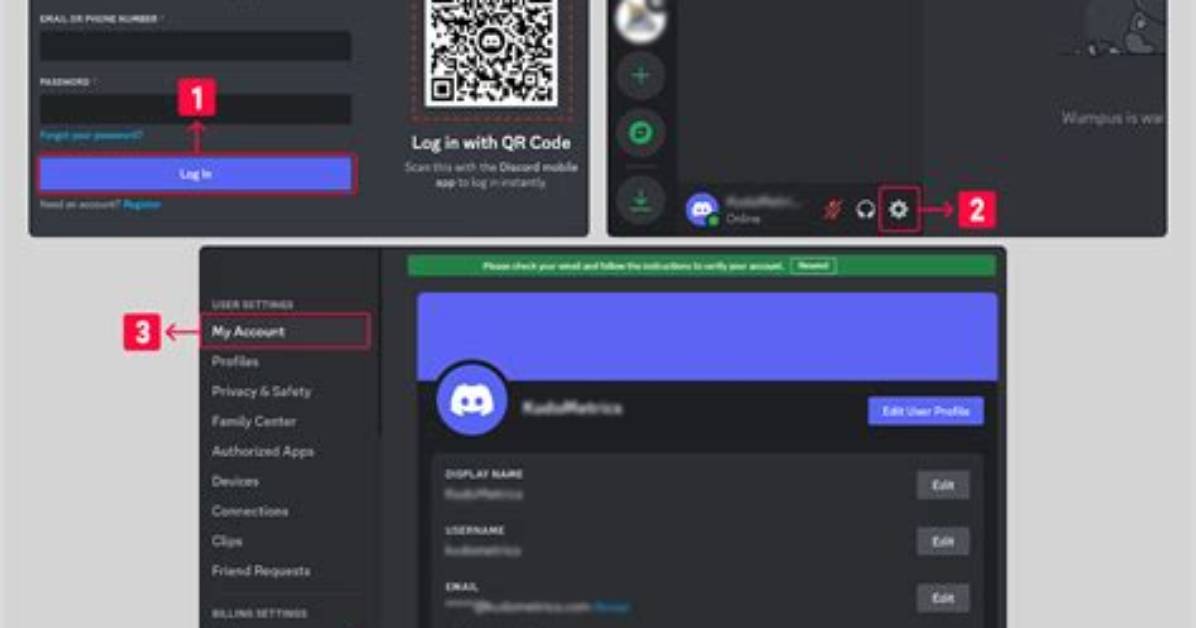
Modern Discord threat groups avoid simple password harvesting forms because two-factor authentication blocks unauthorized sign-ins. Instead, malicious servers use token grabbers and rogue OAuth2 authorization schemes. Recognizing these vectors prevents accidental account compromise.
When joining an unverified InPvP or Mineville portal, watch for these distinct attack patterns:
The first indicator involves external OAuth2 authorization screens. A bot prompts the user to verify by clicking an external link. The redirect opens a Discord authorization window that asks for intrusive permission scopes, such as the ability to join servers on the user's behalf (guilds.join) or view email addresses. Authentic community servers rely on Discord's built-in Community Onboarding screens or simple image-based CAPTCHAs that run entirely inside Discord's native interface.
The second indicator centers on Microsoft account linking scams. Because InPvP operates inside Bedrock, scammers claim that players must "sync their Xbox Live profile" to talk in the Discord server. The provided link directs users to an adversary-in-the-middle phishing site that captures Microsoft credentials, session cookies, and multi-factor approval prompts. This gives the attacker complete control over the victim's Minecraft licenses and linked marketplace assets.
The third indicator is the mobile QR code login trap. Fraudulent bots instruct mobile users to scan a QR code with their Discord camera tool to "prove humanity." In reality, that QR code is Discord's native Remote Auth system. Scanning it transmits your active login session directly to the attacker's workstation, bypassing passwords and 2FA entirely.
Marcus Vance is a cybersecurity auditor and technology writer dedicated to educating the public about online safety, data privacy regulations, enterprise security, and emerging cyber threats.
