Behind Tiktok Business Center: Managing Tiktok Shop Risks and Permissions
 By Robert Thorne
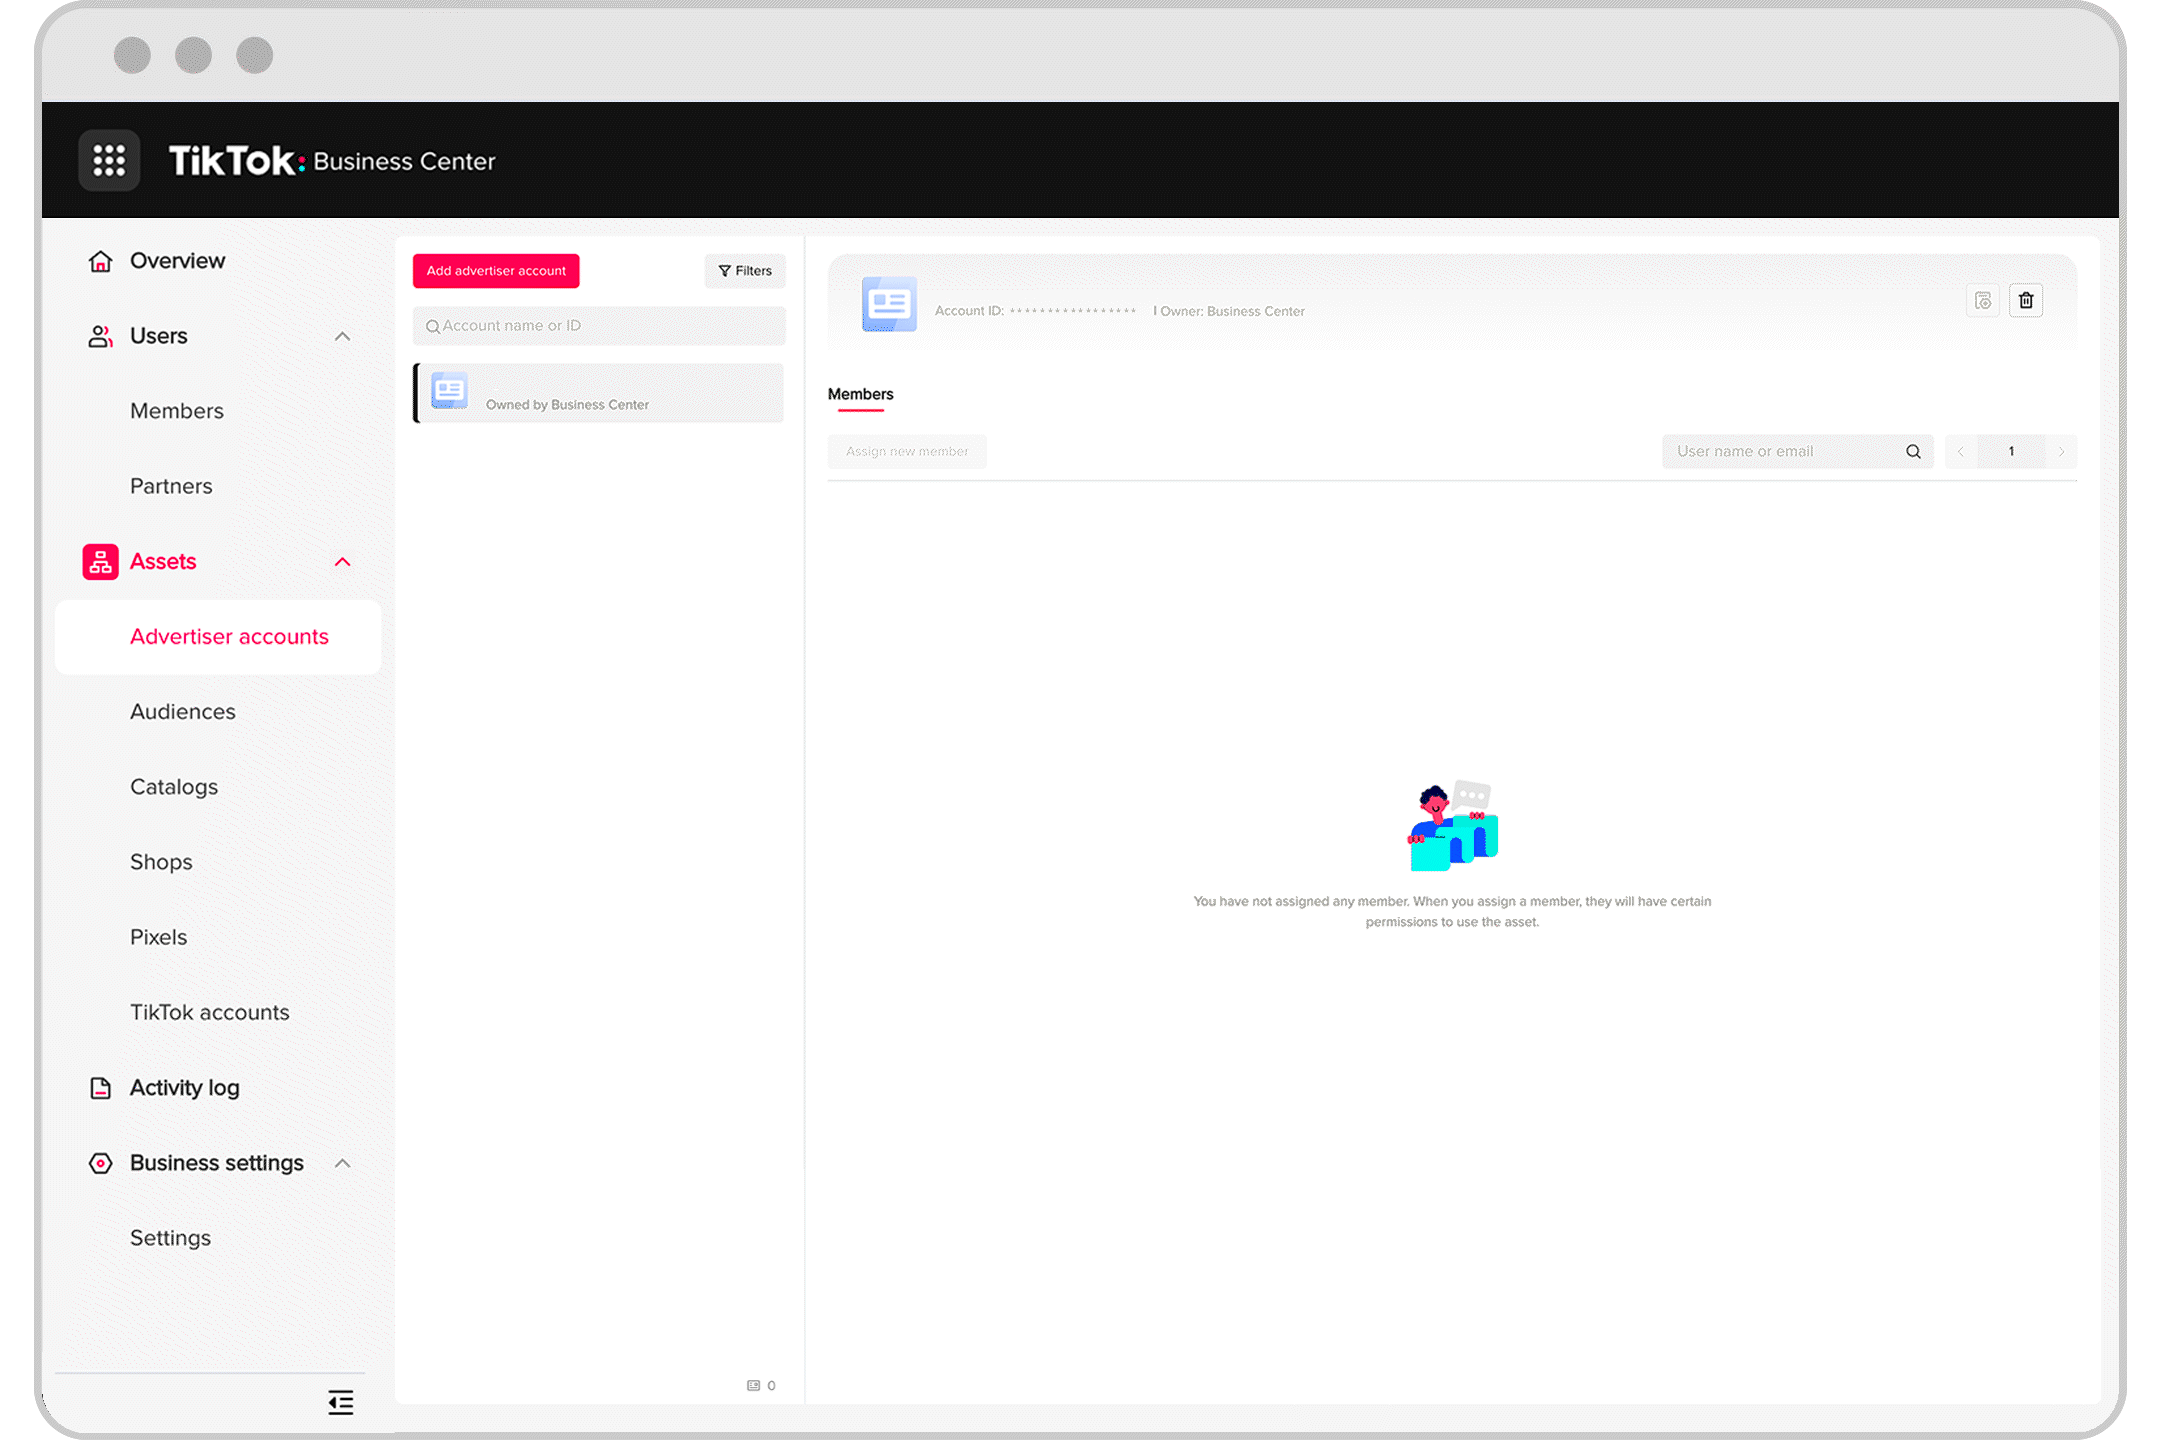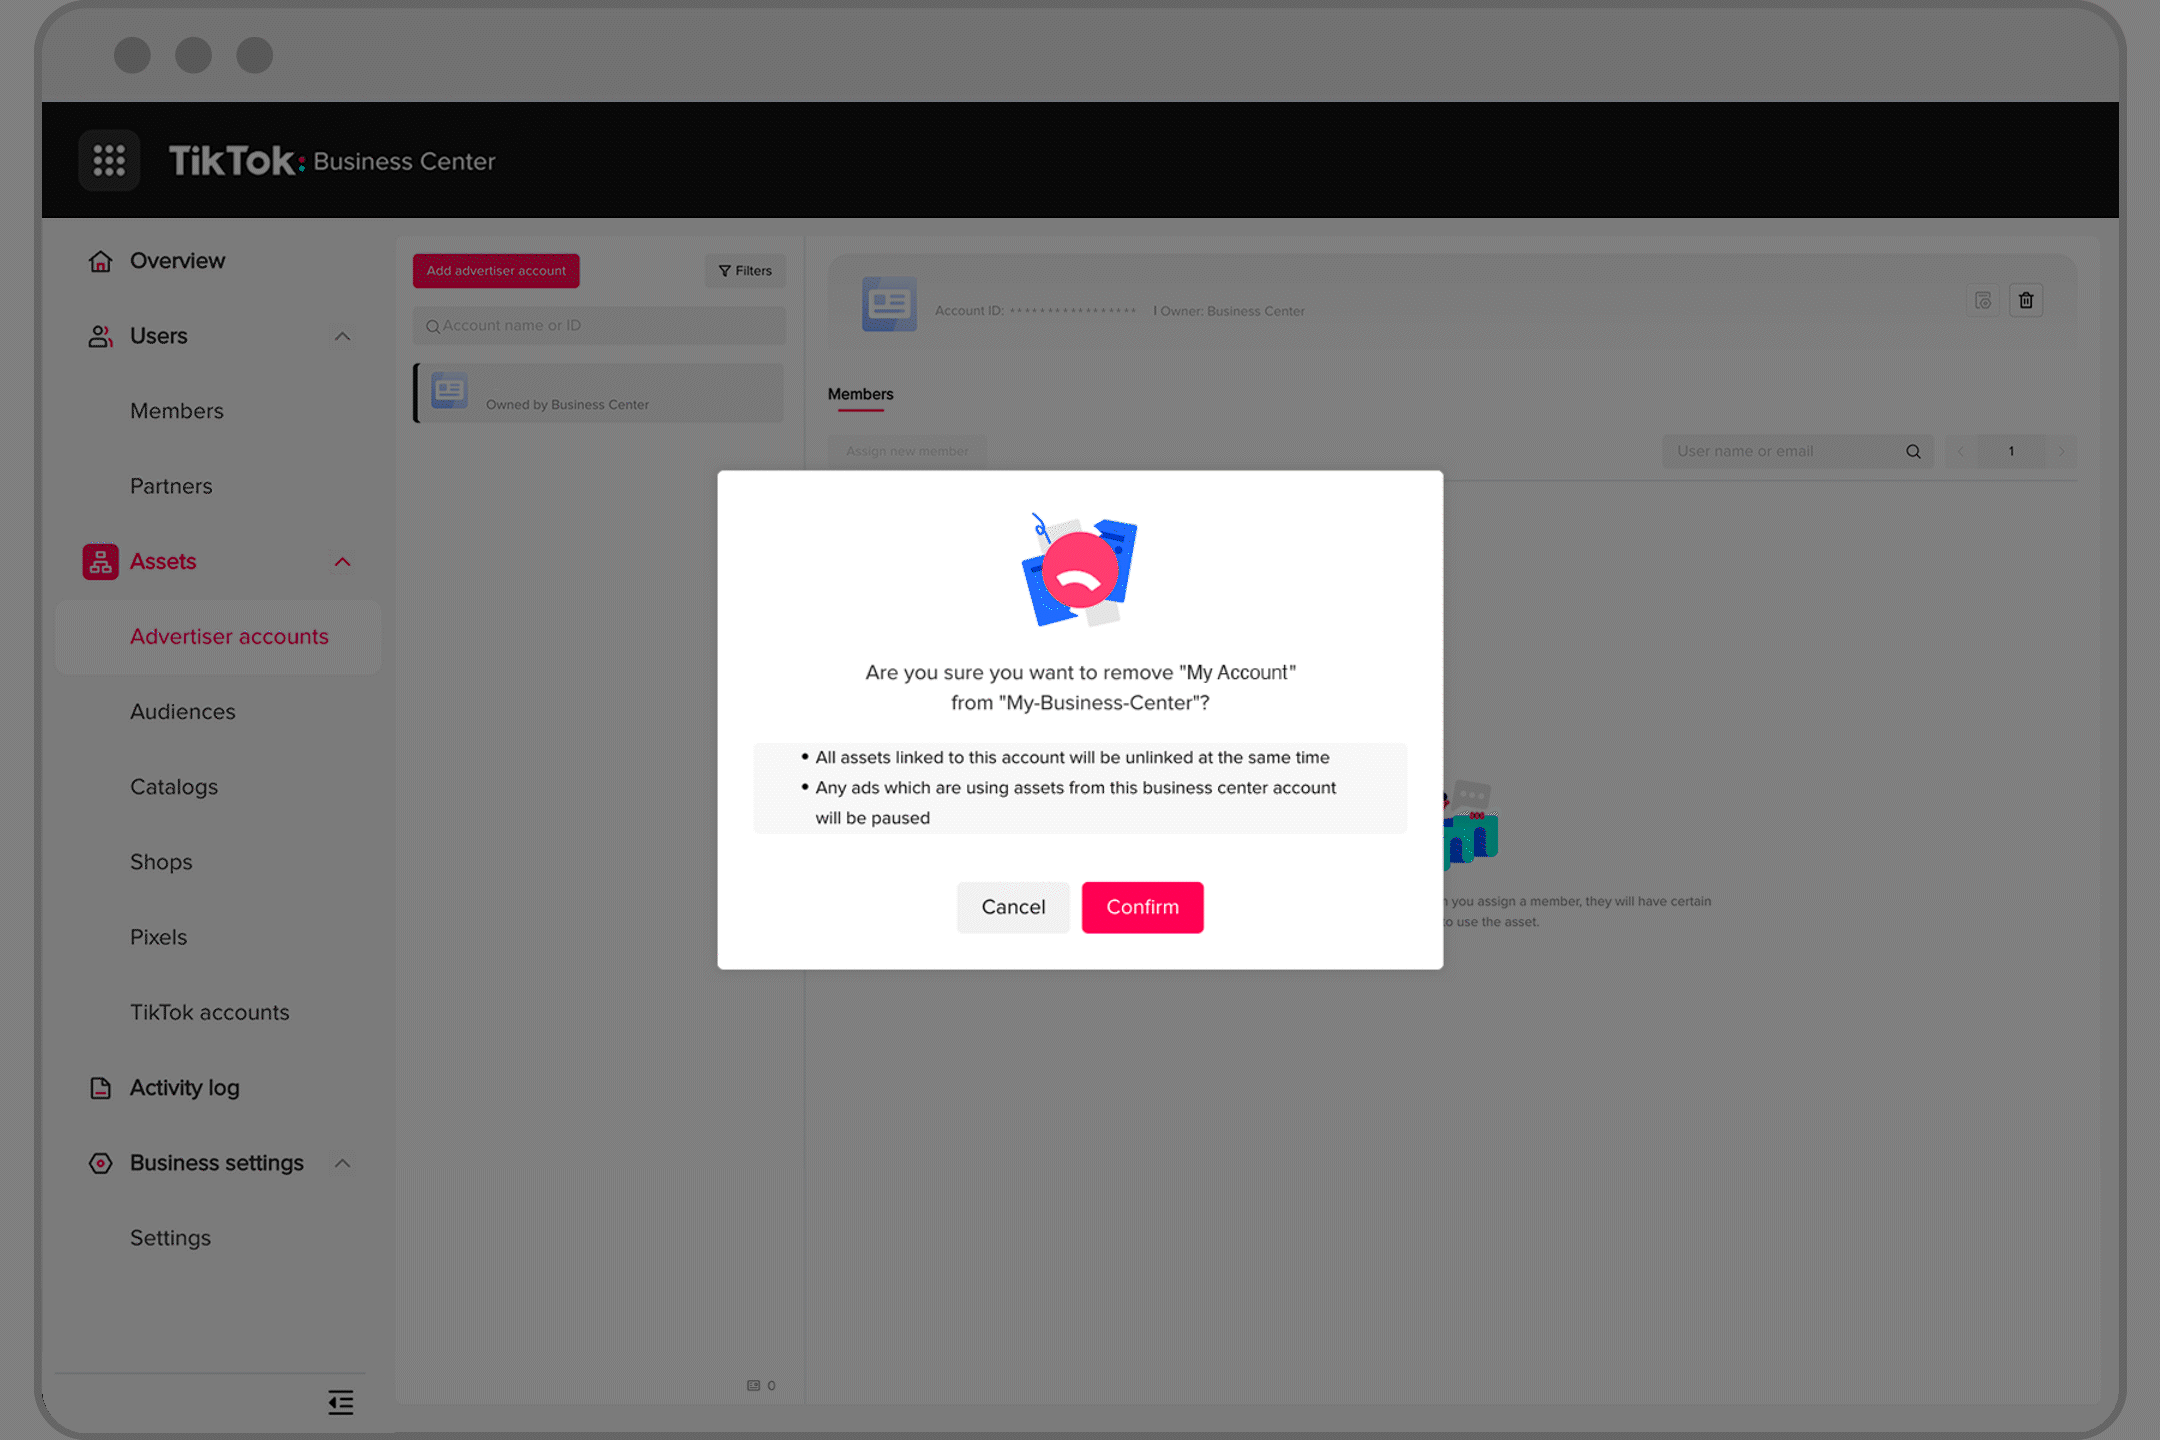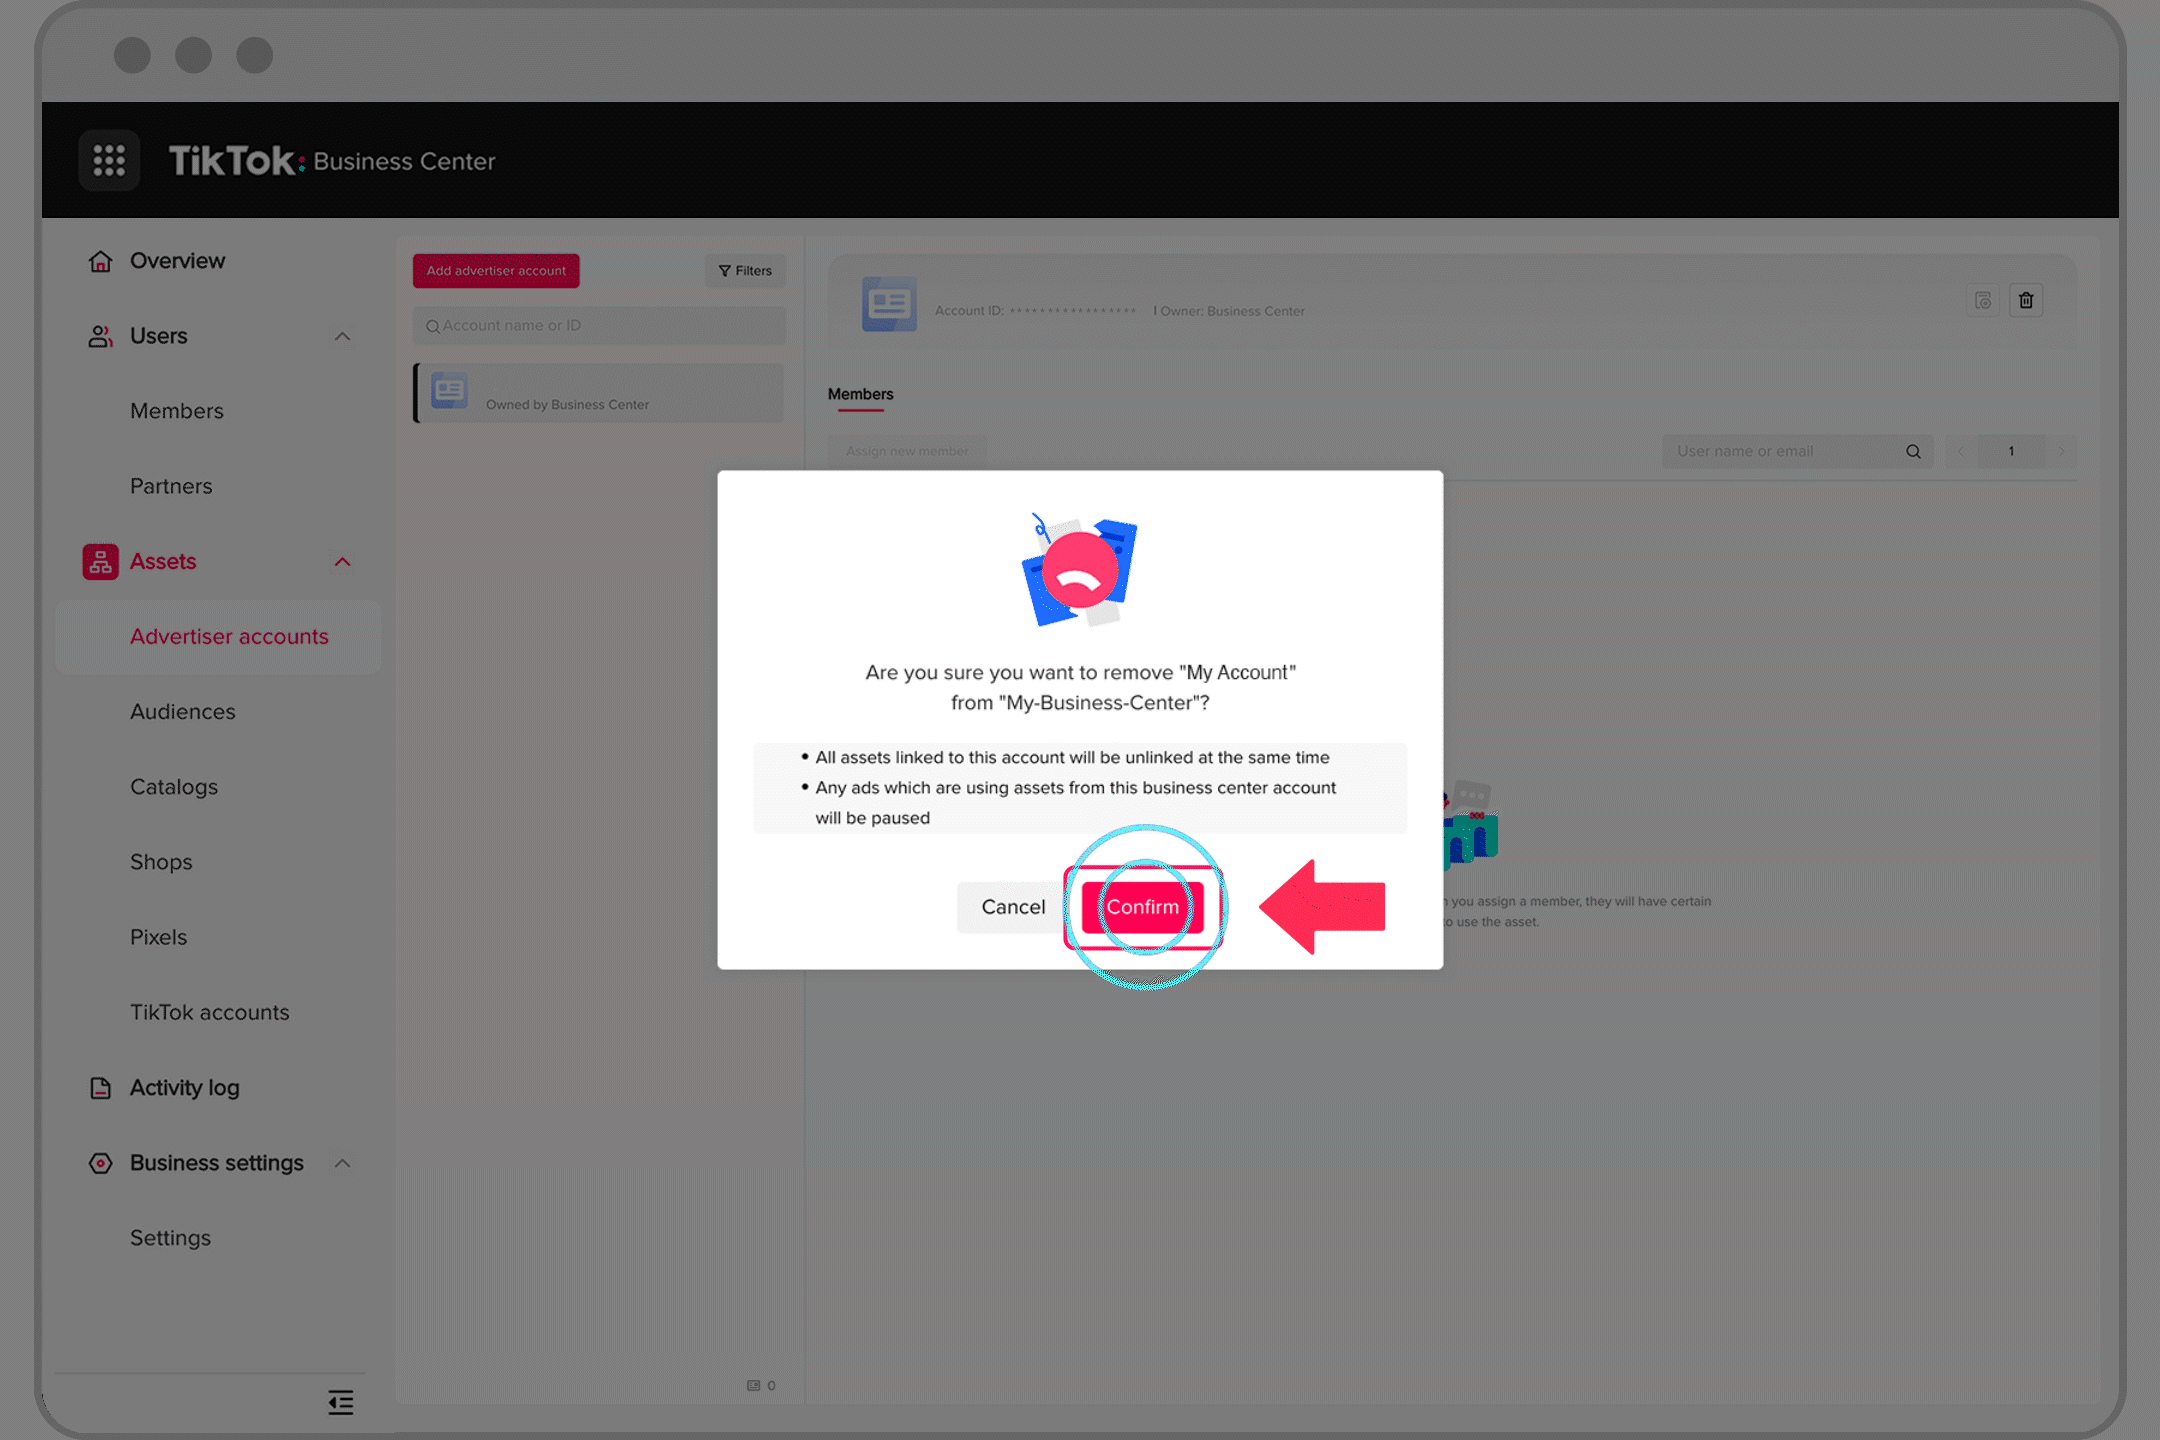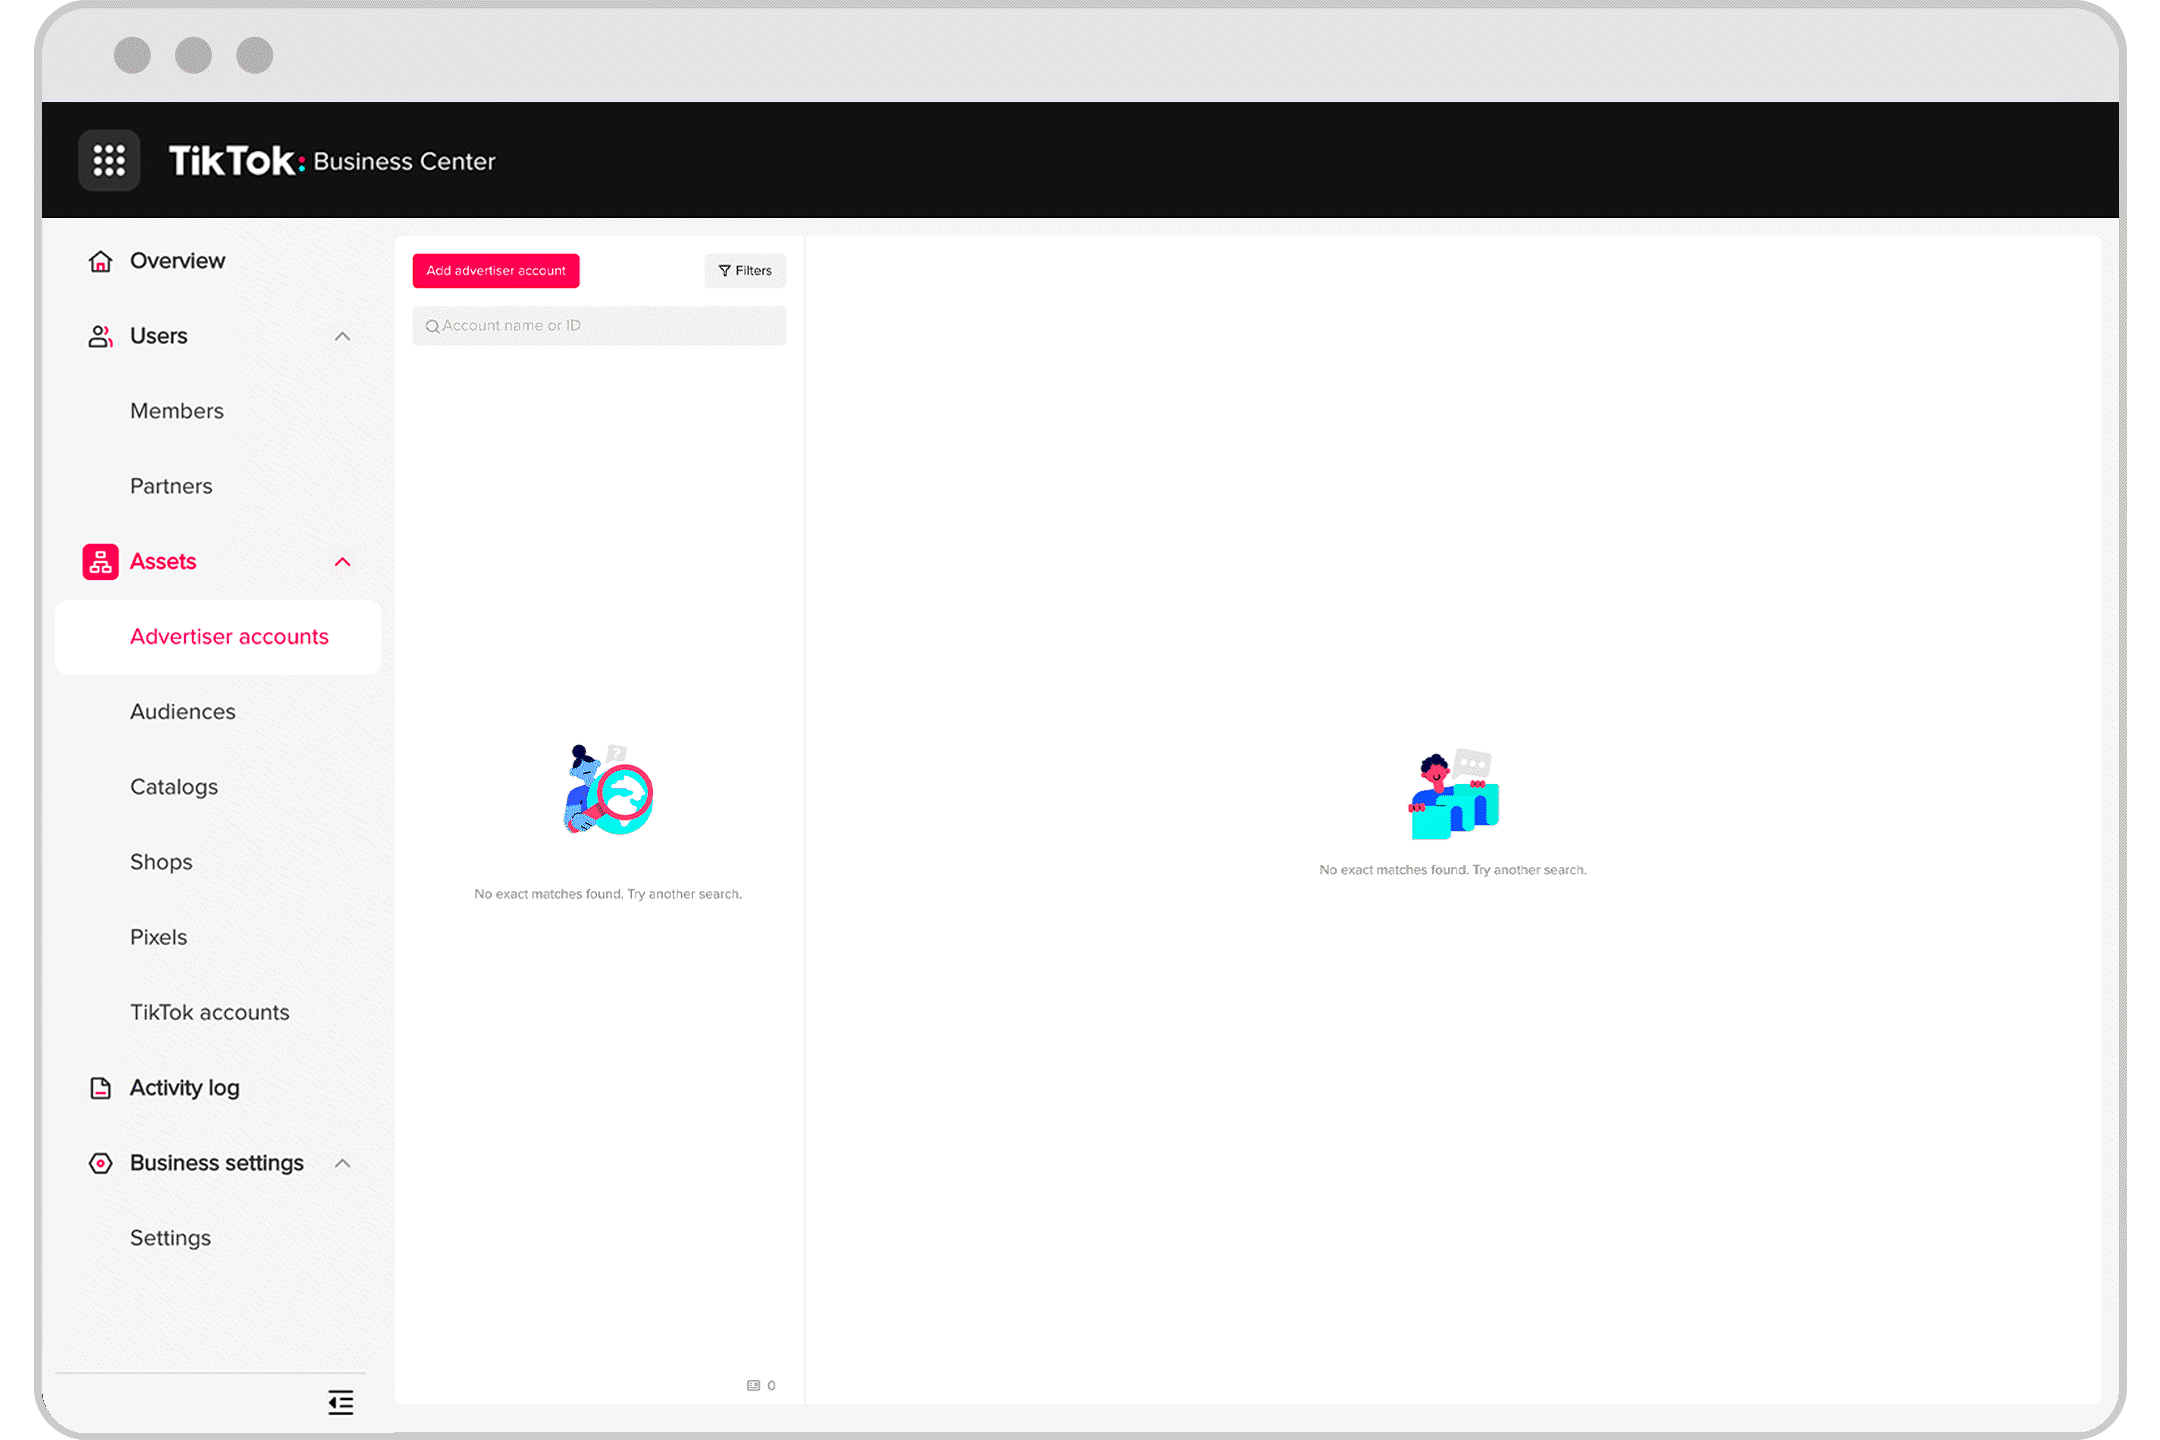
Direct-to-consumer data privacy inside social commerce ecosystems has drawn significant scrutiny. Operational security reporting has repeatedly exposed how unmonitored tracking configurations capture excessive customer telemetry across consumer-facing platforms. Within the Business Center, data security settings dictate how the TikTok Pixel and Events API interact with external site traffic and native purchases.
Brands must configure advanced data-matching tools carefully to comply with state and international privacy regulations. Allowing unfiltered customer parameter pass-throughs without clear user consent banners invites immediate regulatory penalties. Digital compliance officers should regularly audit pixel event triggers, ensuring sensitive personal data, such as raw billing addresses or unhashed phone numbers, is stripped before event signals exit local customer containers.
High-volume merchants operating on social marketplaces face growing liabilities around brand indemnity and supply chain defaults. Leading commercial underwriters now require social merchants scaling past $5M in annual GMV to carry comprehensive cyber liability policies alongside product liability insurance. These policies increasingly mandate strict internal controls, including mandatory two-factor authentication (2FA) enforcement across all Business Center members, logged quarterly permission audits, and the immediate decommissioning of dormant third-party partner permissions.
Robert Thorne covers electric vehicle innovations, autonomous driving systems, global mobility trends, and automotive engineering developments.
